Gbemi Shield
Cybersecurity

I secured a 500-room hotel's IoT water system. I learned everything from threat analysis, IoT networking technologies (MQTT), and how to give understandable defense policies and vulnerability overviews. I secured this pipeline using mTLS, hashing, and Isolation Forest to flag anomalies
Location:
Remote
Role:
Cybersecurity Extern
Year:
2026


Explore the full story –
Challenge
Grand Marina, a simulated 500-room hotel, ran its water management system on plain MQTT with zero security, streaming live sensor data from 3 device zones (Main Building, Pool & Spa, Kitchen & Laundry) with no encryption, no device authentication, and no protection against replayed or tampered messages. Every attack I simulated against it succeeded
Objective
Harden the pipeline in stages, moving from plaintext MQTT to one-way TLS, then mutual TLS with per-device certificates, then a three-layer replay defense (HMAC-SHA256, timestamp freshness, sequence counters), and finally an Isolation Forest model to catch anomalies none of those rules would flag. I also ran a full STRIDE threat model and wrote security reports translating the findings for a non-technical hotel GM
Results
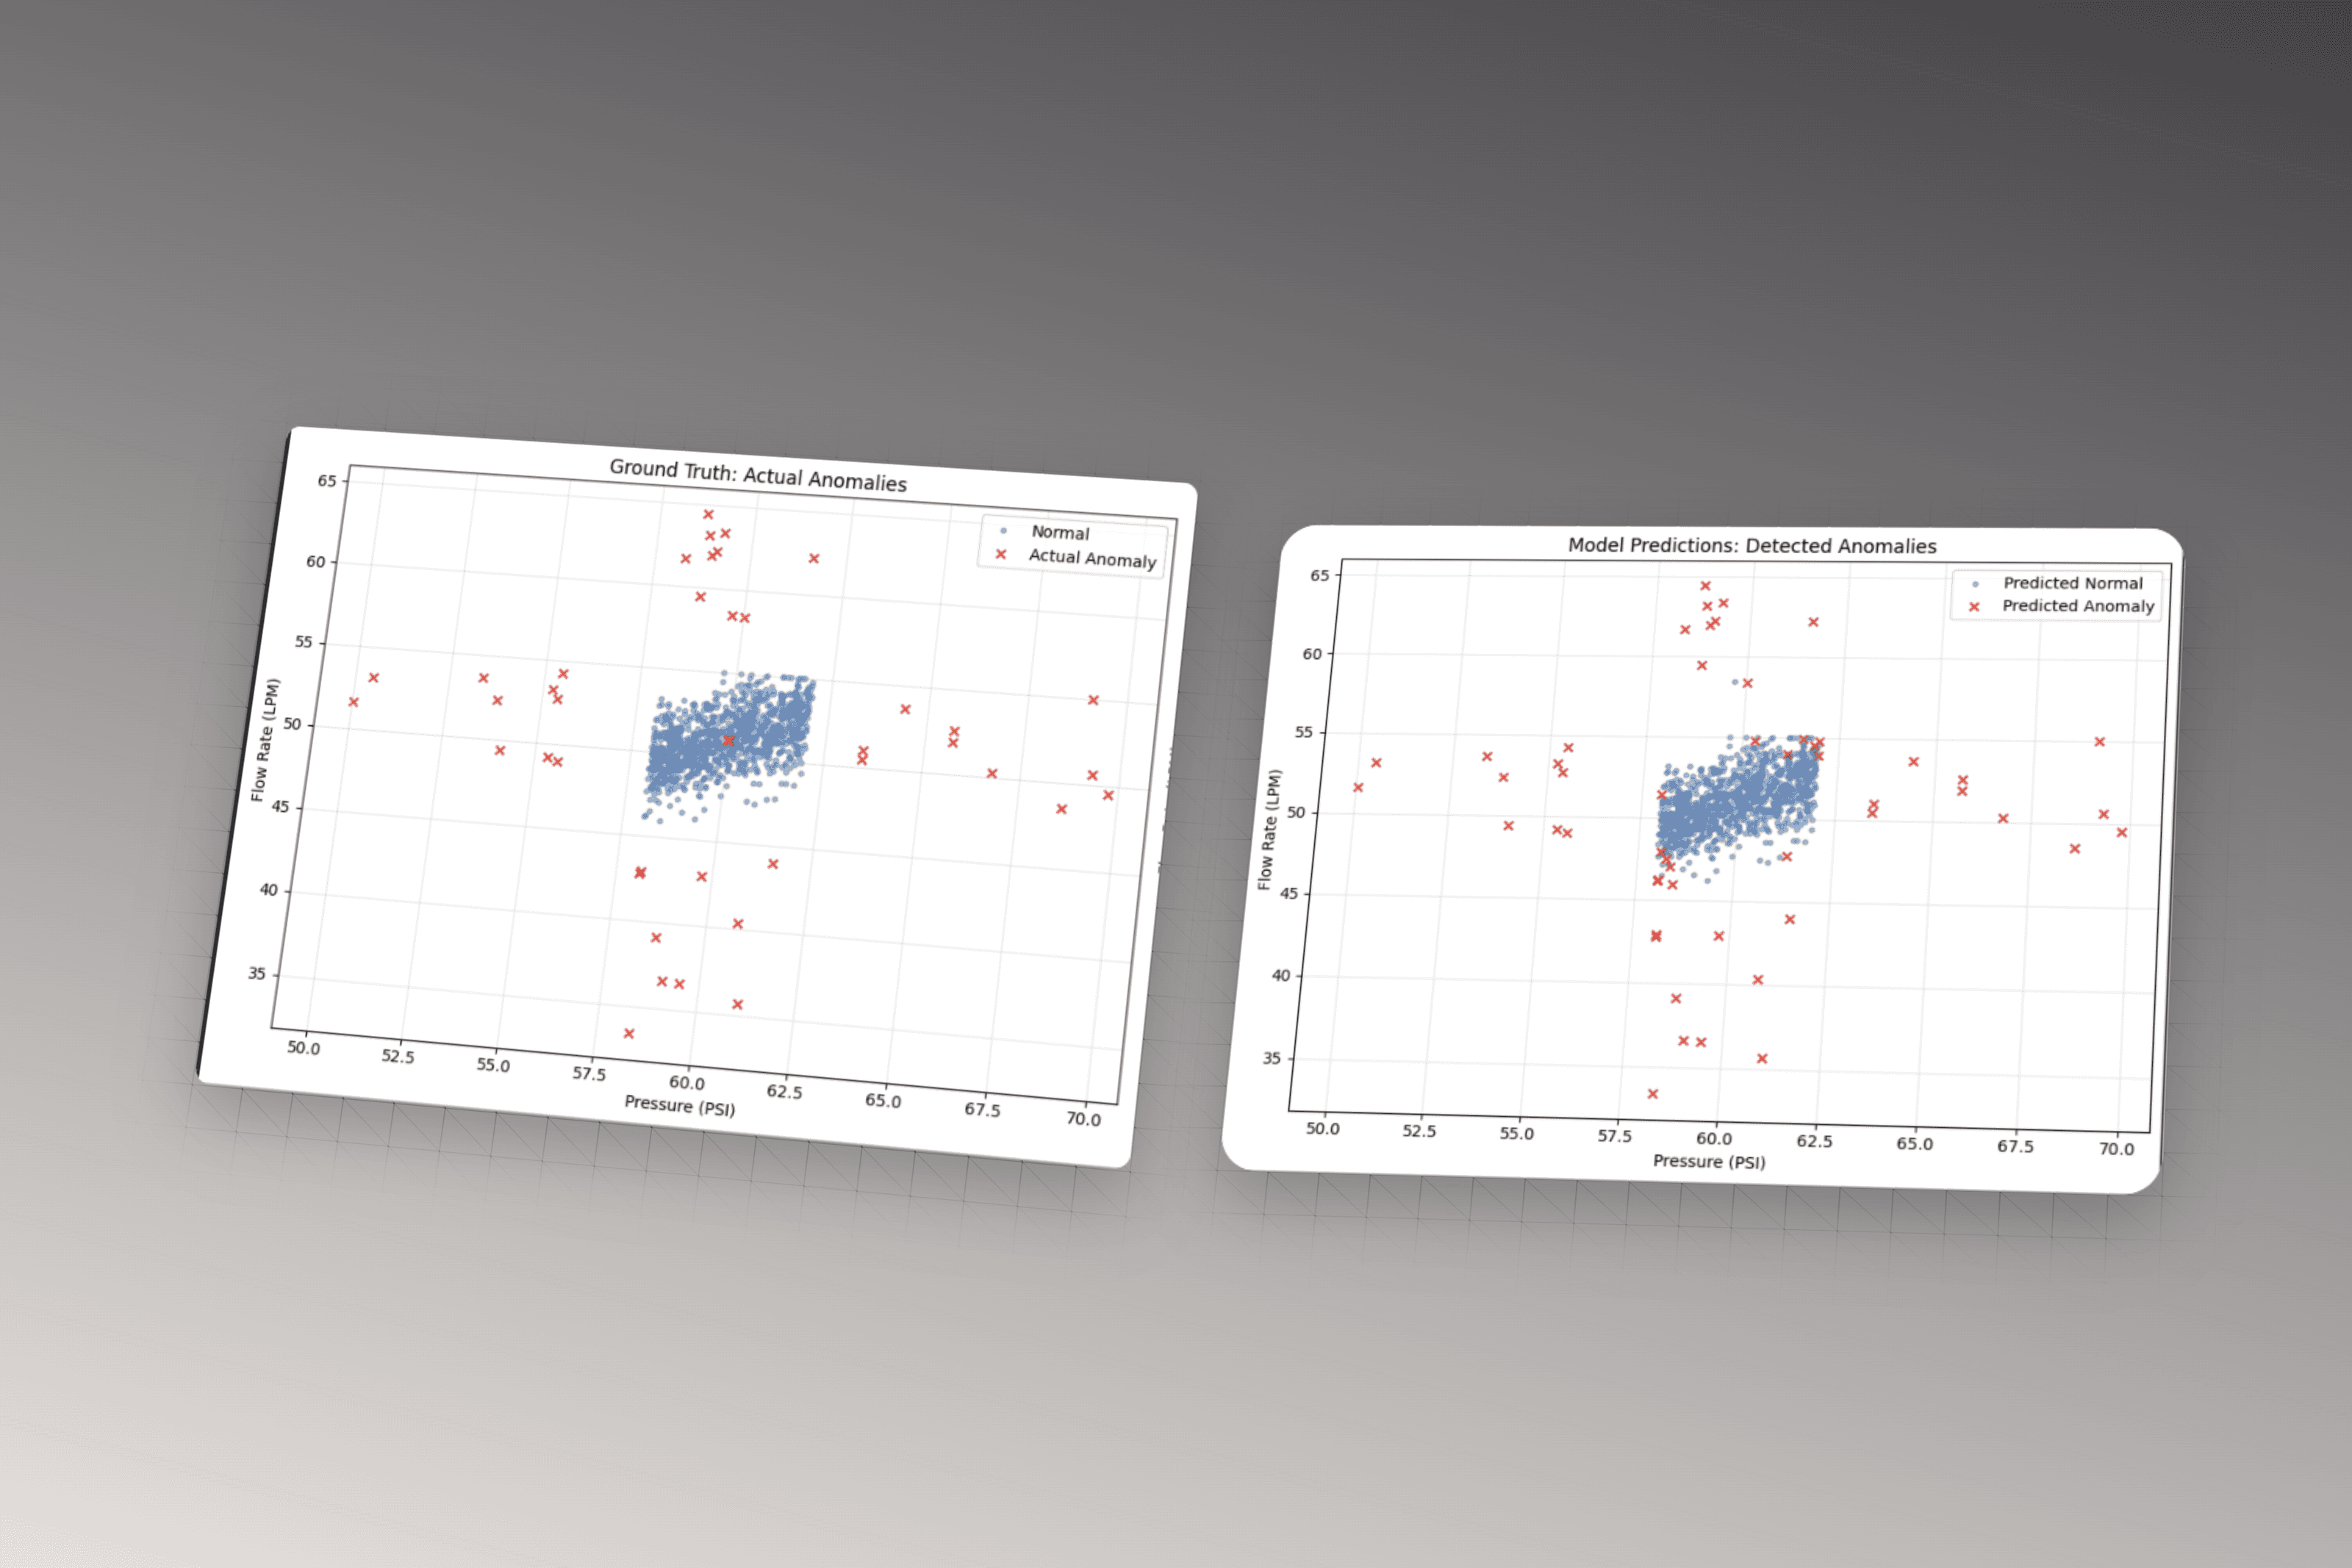
All three replay defenses combined hit a 100% rejection rate across immediate, delayed, and modified replay attacks, up from 0% on the undefended baseline. The Isolation Forest model added a second layer, catching behavioral anomalies that passed every rule check, at 0.74 precision / 0.78 recall / 0.76 F1. I built a live GbemiShield dashboard to visualize it all in real time, and finished in the top 10% of learners for the externship